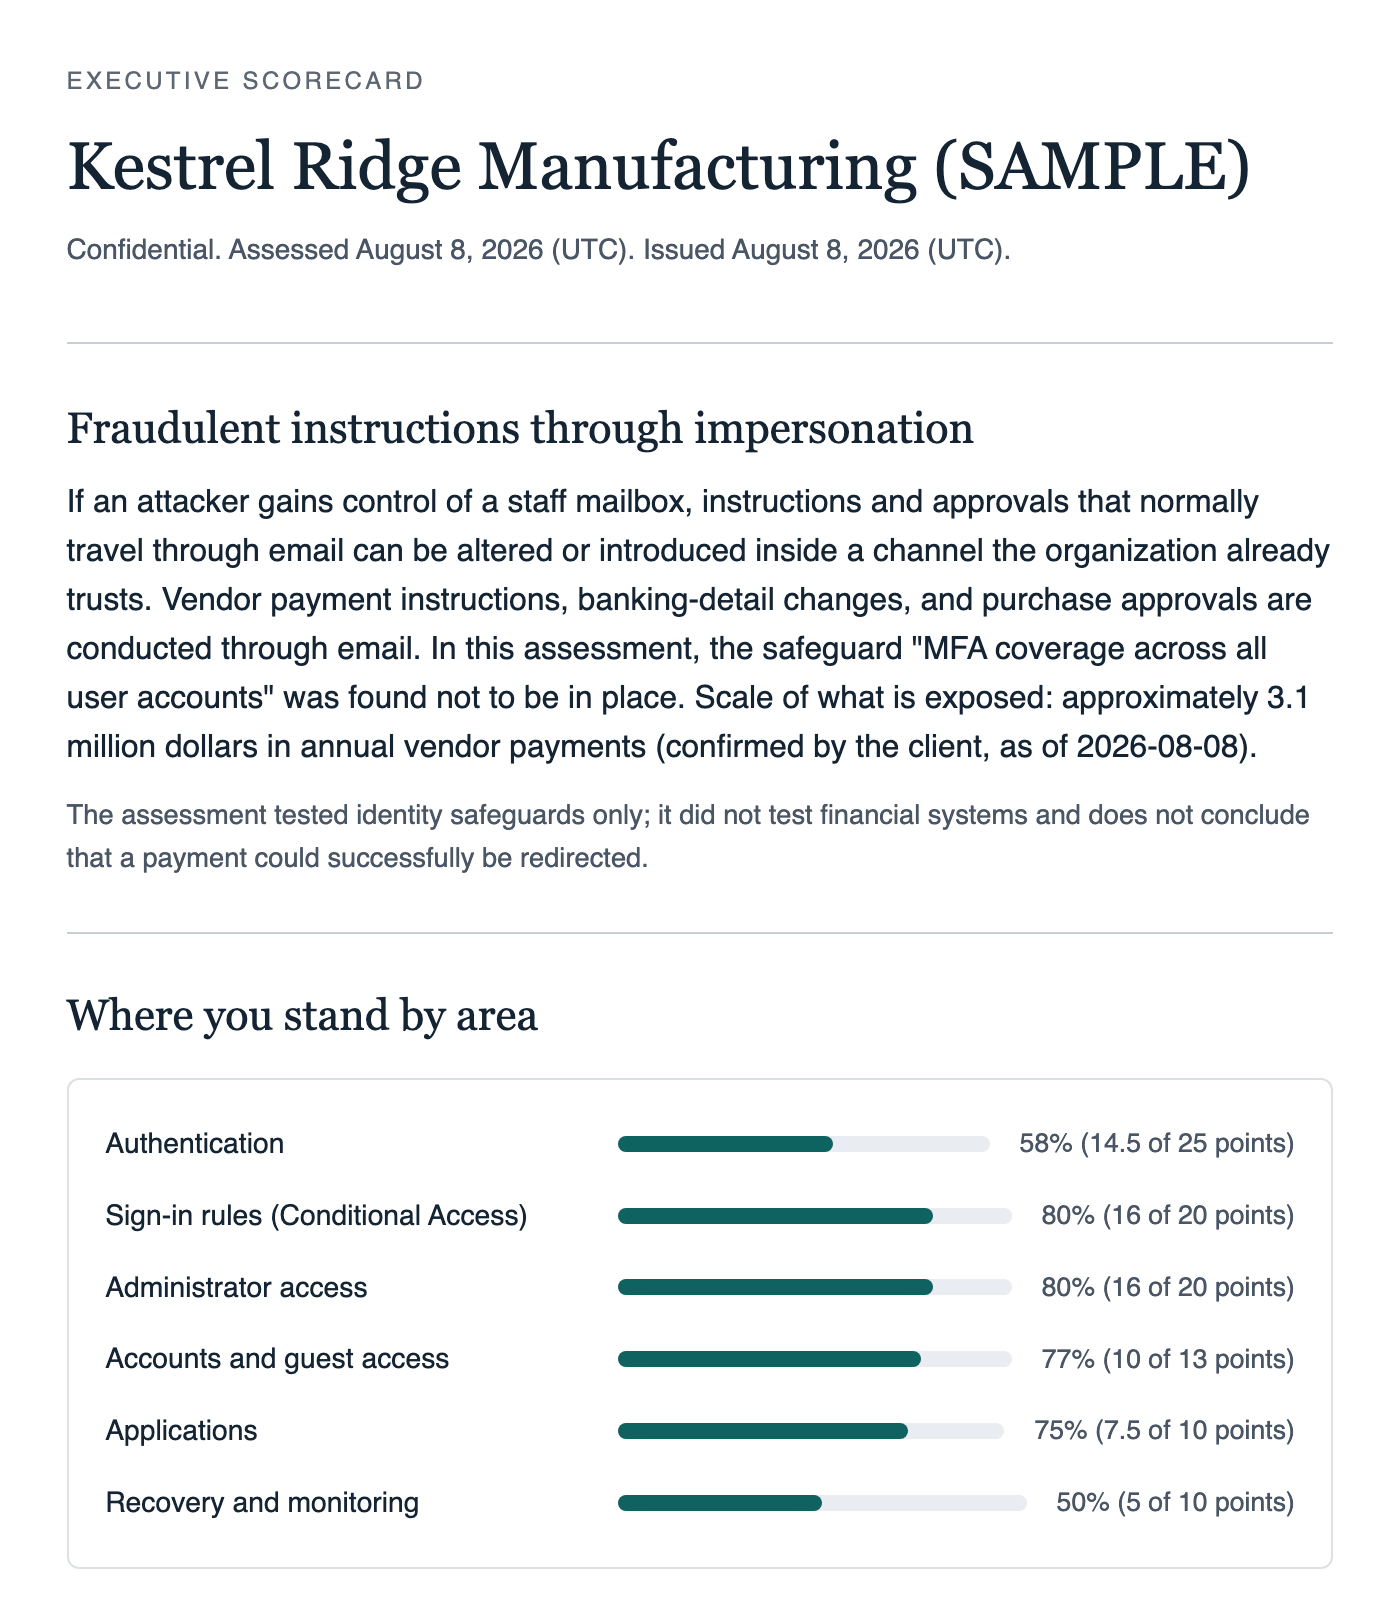
An excerpt from the executive scorecard prepared for Kestrel Ridge Manufacturing (SAMPLE), an invented company, assessed August 8, 2026: the same scenario and bars as the scorecard image, plus the plan's first priorities, as text.
Business scenarios connected to current findings
Fraudulent instructions through impersonation. If an attacker gains control of a staff mailbox, instructions and approvals that normally travel through email can be altered or introduced inside a channel the organization already trusts. Vendor payment instructions, banking-detail changes, and purchase approvals are conducted through email. In this assessment, the safeguard "MFA coverage across all user accounts" was found not to be in place. Scale of what is exposed: approximately 3.1 million dollars in annual vendor payments (confirmed by the client, as of 2026-08-08; a fictional figure).
The assessment tested identity safeguards only; it did not test financial systems and does not conclude that a payment could successfully be redirected.
Where you stand by area
- Authentication58% (14.5 of 25 points)
- Sign-in rules (Conditional Access)80% (16 of 20 points)
- Administrator access80% (16 of 20 points)
- Accounts and guest access77% (10 of 13 points)
- Applications75% (7.5 of 10 points)
- Recovery and monitoring50% (5 of 10 points)
What to do first
The issued remediation plan sequences the work so recovery safeguards land before any change that could lock anyone out. Its first priorities are:
- Emergency-access accounts exist, are protected, and are tested
- MFA coverage across all user accounts
- Authentication methods policy is managed and weak methods are disabled
- Conditional Access policies specifically protect administrator sign-ins
- Administrators use separate accounts for privileged work