Microsoft 365 Identity Security Assessment
A fixed-fee, read-only review of your Microsoft 365 tenant. Evidence for every finding, a prioritized fix plan, and approved remediation options. Delivered virtually or on site, anywhere in the US.
Most Microsoft 365 breaches start with identity.
A sign-in that should have been challenged. An account with more access than it needs. A setting nobody has looked at since the tenant was created. This assessment reviews those controls setting by setting and shows you exactly what to fix first. The controls reviewed map to the CISA SCuBA baseline for Microsoft Entra ID and the derived NIST SP 800-53 Rev. 5 controls.
What you get
A written report with evidence
Evidence for every finding, not a scanner printout.
A prioritized fix plan
What is exposed, why it matters, and the order to fix it.
A 90-minute readout
The findings walked through with your team or your IT provider.
Approved remediation options
If you want the fixes done for you, we shape that together and you approve it before anything starts.
At a glance
- Fixed fee, scoped after the discovery call
- Read-only access you grant and can revoke
- No software installed on your devices
- One 90-minute readout against prepared deliverables
- Written so your IT provider can act on it
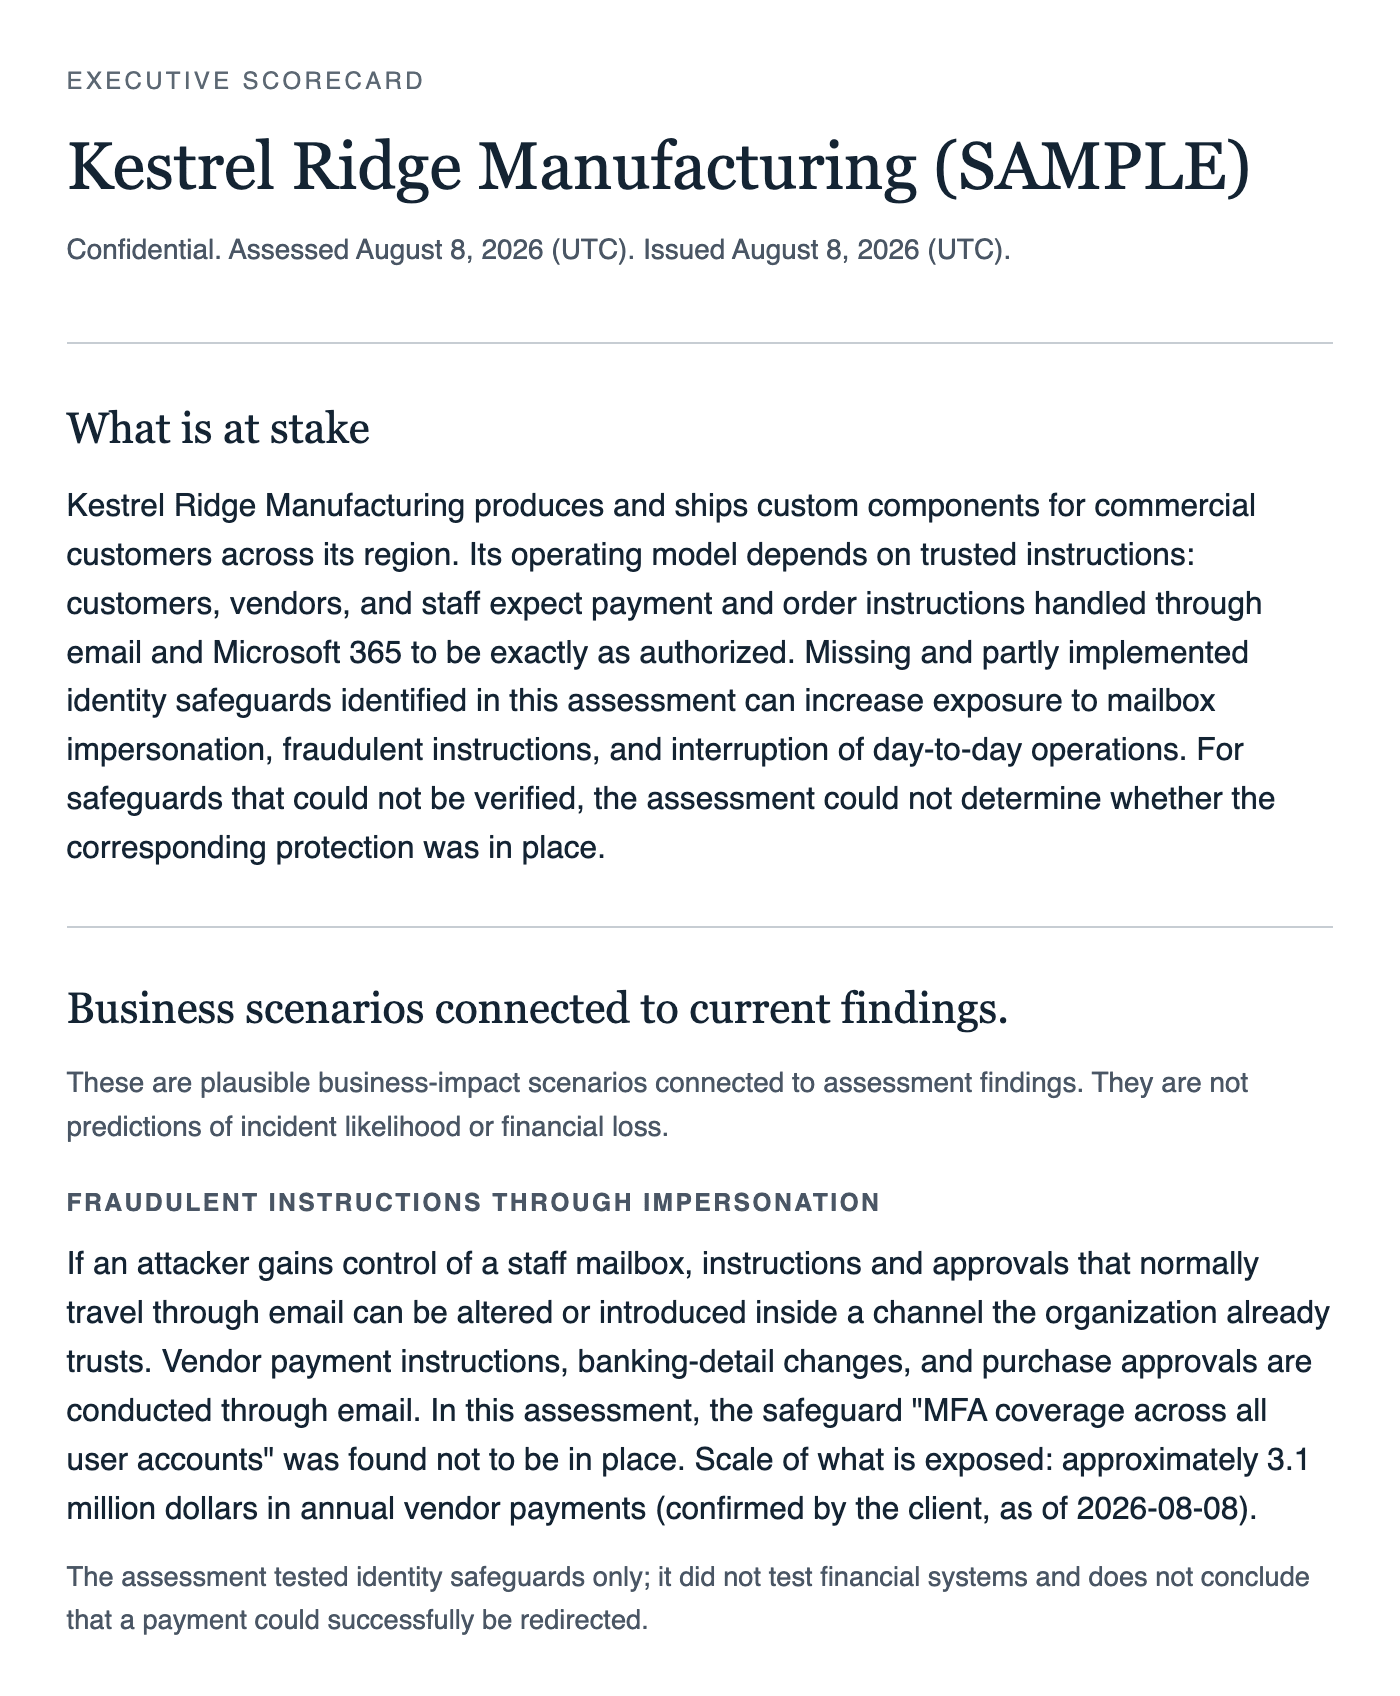
The executive scorecard, page by page.
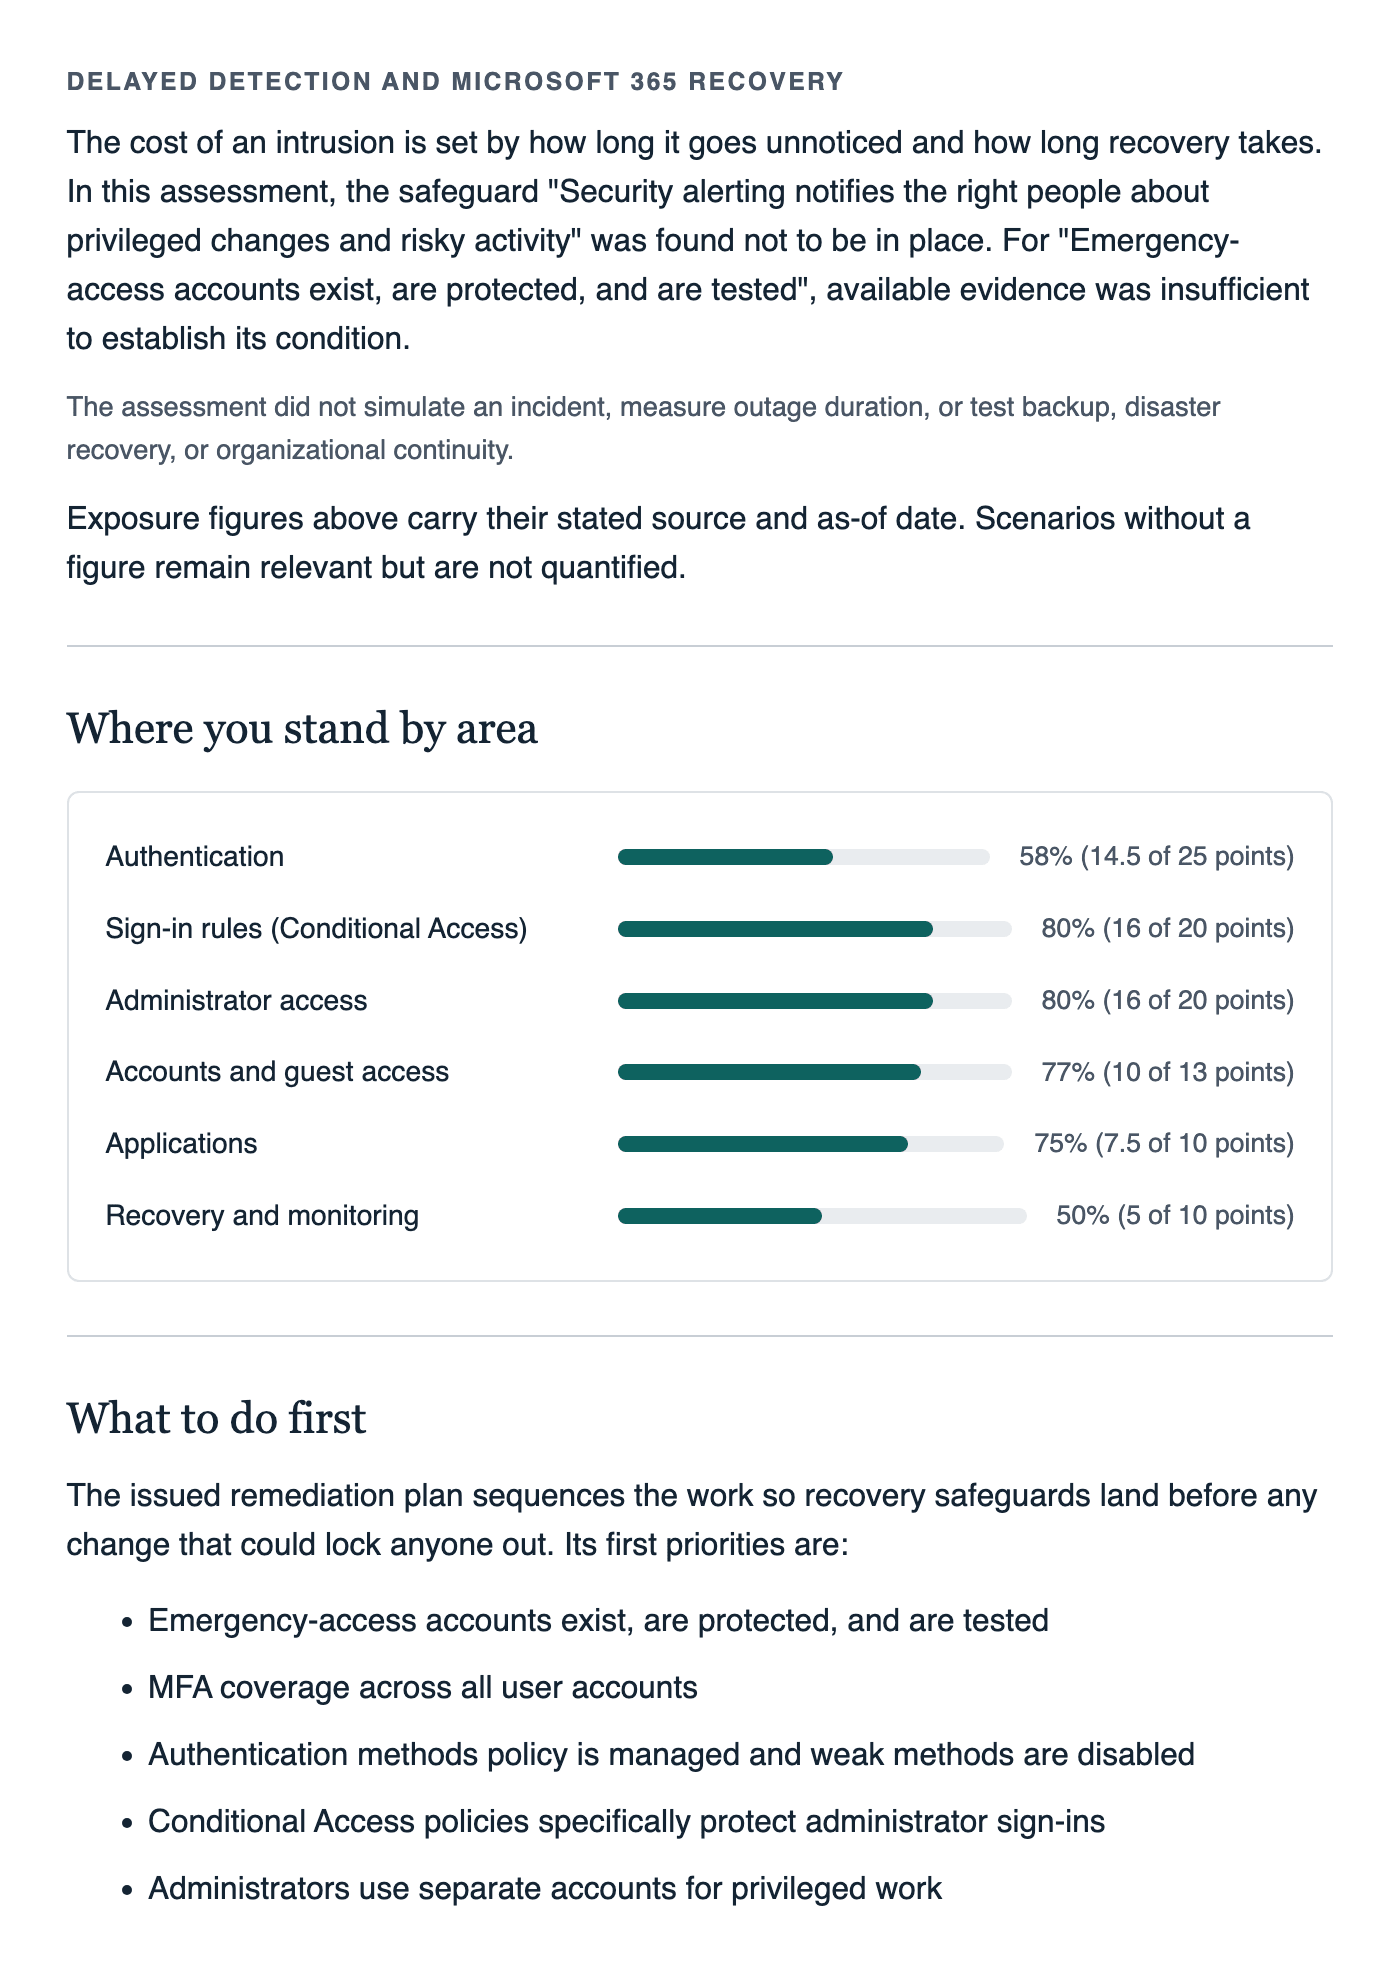
Written for an owner or a board, not for the help desk. Two pages from a sample scorecard prepared for an invented company.
What is at stake
Your operating model in plain language: what the organization depends on, and what the findings expose.
Business scenarios
Each scenario ties a finding to a business outcome, with the source and date of every figure and a stated boundary.
Where you stand
Six areas scored on safeguard coverage. Not a compliance certification.
What to do first
The first steps in order, sequenced so recovery lands before any change that could lock anyone out.
Four steps, no surprises.
Discovery call
A 30-minute conversation to confirm scope and quote a fixed fee. No obligation.
Access
You grant read-only access to your tenant. No software touches your devices, and you can revoke the access at any time.
Review
We examine your identity and access configuration setting by setting and collect evidence as we go.
Findings
When collection is complete, you receive the report, the fix plan, and the scorecard, then one 90-minute readout with your team or your IT provider.
Organizations that need a clear answer.
Organizations that run on Microsoft 365 and need a clear answer, from lean nonprofits to multi-site companies: for a cyber insurance questionnaire, a board or leadership question, a customer security review, or a concern about account compromise. If you have an IT provider, the report is written so they can act on it directly.
For businesses and organizations only. We do not provide consumer or personal account support.
Who delivers it
Mount Xion Technologies is a veteran-owned cybersecurity firm in San Antonio, Texas. Our principal directed IT and cybersecurity for a $1B+ organization and served in the USAF, and every engagement is principal-led, from first call to final report. A bench of vetted senior practitioners works alongside on delivery and peer-reviews the findings, so every report reflects more than one set of experienced eyes.
Credentials across the practice include CISSP, PMP, SSCP, CompTIA CySA+, CompTIA Security+, CompTIA Project+, and ITIL 4. We treat credentials as table stakes: the deliverables stand on evidence collected from your tenant, not on letters after names.
Pricing
Fixed fee, scoped after the discovery call. You will know the full cost before any work begins.
Common triggers
- A cyber insurance questionnaire you cannot answer confidently
- Your payment processor's annual PCI self-assessment questionnaire
- A board or leadership request for a security picture
- A customer security review
- A concern that an account was compromised
- A general posture check before something goes wrong
Request a 30-minute discovery call.
Tell us a little about your organization and we will confirm scope and quote a fixed fee on the call.